Open to Work — UK SOC Analyst Roles
BLOG Cyber Insight · Threat Research ↗

Poorna
Sujampathi

SOC Analyst · Incident Response · Threat Detection

SOC Analyst with 2.5+ years across Tier 1 & Tier 2 operations in Banking, Aviation & Telecom.
MSc Cyber Security · Hatfield, UK

Microsoft Sentinel CrowdStrike Falcon IBM QRadar NetScout DDoS Splunk Python Automation
2.5+ Years SOC Experience Tier 1 & Tier 2
1K+ Daily Alerts Triaged 100% SLA Maintained
30% Efficiency Gain Python Automation
3 Industry Sectors Banking · Aviation · Telecom
MSc Cyber Security NCSC Certified

A security professional
with a passion for defence.

SOC Analyst with 2.5+ years of hands-on experience in Tier 1/2 Security Operations Centre environments across banking, aviation, and telecommunications. Experienced in 24/7 security monitoring, high-volume alert triage, incident detection and response, threat hunting, log analysis, and IOC investigation.

Hands-on expertise with Microsoft Defender, CrowdStrike, IBM QRadar, McAfee SIEM, and Microsoft Sentinel — with a strong focus on MITRE ATT&CK, detection engineering, correlation rule tuning, SOC automation, and Python/KQL scripting.

Proven ability to investigate and escalate security incidents within SLA requirements while developing automation and detection capabilities to improve SOC efficiency. Completed an MSc in Cyber Security at the University of Hertfordshire. Focused on SOC and Incident Response opportunities in the UK.

Beyond live operations, I actively author and publish Cyber Insight (The Digital Watch) — an independent threat intelligence and security research publication breaking down real-world enterprise breaches, emerging AI deception, synthetic voice cloning, and digital safety in clear, jargon-free English.

Total Experience
2.5+ Years (Tier 1 & Tier 2)
Alert Triage & SLA
1,000+ Daily Alerts (100% SLA)
Education
MSc Cyber Security (NCSC Certified)
Location
Hatfield, United Kingdom

Where I've worked
and what I've achieved.

Jun 2023 – Sep 2024 Air Arabia · UAE

SOC Analyst (Tier 2)

★ Best Performance Award 2023
Microsoft Defender Incident Response SOC Automation Rule Tuning NOC Collaboration
  • Alert Triage & Incident Response: Monitored and triaged 1,000+ daily security alerts across enterprise network and endpoint environments, investigating high-severity threats within target SLA timelines.
  • SOC Automation & Optimization: Engineered custom automation tools to streamline incident workflows and improve overall SOC operational efficiency.
  • Threat Detection & Rule Tuning: Executed threat detection using Microsoft Defender and tuned alert correlation rules to reduce false positives.
  • Cross-Functional Incident Escalation: Collaborated closely with NOC teams to investigate, contain and escalate critical incidents efficiently.
  • Key Achievement: Awarded Best Performance Award (2023) for outstanding contributions to SOC monitoring and incident handling.
Feb 2023 – May 2023 Nations Trust Bank · Sri Lanka

Information Security Analyst (SOC)

McAfee SIEM CrowdStrike EDR Forcepoint DLP NetScout Arbor IOC Investigation SOC Playbooks
  • SIEM & EDR Operations: Performed real-time security event analysis, monitoring and threat correlation using McAfee SIEM and CrowdStrike EDR.
  • Live Attack Mitigation: Detected and successfully mitigated a live targeted DDoS attack, protecting critical banking operations from disruption.
  • Incident Investigation & Reporting: Executed end-to-end incident investigations, analysed Indicators of Compromise (IOCs), and authored post-incident reports.
  • DLP Monitoring & Playbook Development: Monitored data exfiltration attempts using Forcepoint DLP and updated standard SOC playbooks to improve response procedures.
Feb 2022 – Feb 2023 SLT-Mobitel · Sri Lanka

Information Security Analyst Intern (SOC)

IBM QRadar CyberArk PAM WAF DDoS Detection
  • Log Analysis & Threat Identification: Monitored security logs using IBM QRadar SIEM to identify anomalous behaviour and potential security breaches.
  • Tier 1 SOC Workflows: Supported daily SOC operations, including initial alert triage, IOC verification and threat escalation.
  • Perimeter & Access Defence: Assisted in detecting DDoS attacks and monitored web traffic and privileged access via WAF and CyberArk PAM.

Technical expertise across
the security stack.

Security Operations (SIEM/EDR)

  • Microsoft Sentinel (Azure Sentinel)
  • IBM QRadar
  • McAfee SIEM
  • FortiAnalyzer
  • CrowdStrike Falcon (EDR)
  • Microsoft Defender for Endpoint
  • Cortex XDR

Threat Detection & Analysis

  • Alert Triage & Incident Response
  • Threat Intelligence Analysis
  • IOC Investigation & Enrichment
  • Threat Hunting
  • Detection Engineering & Rule Tuning
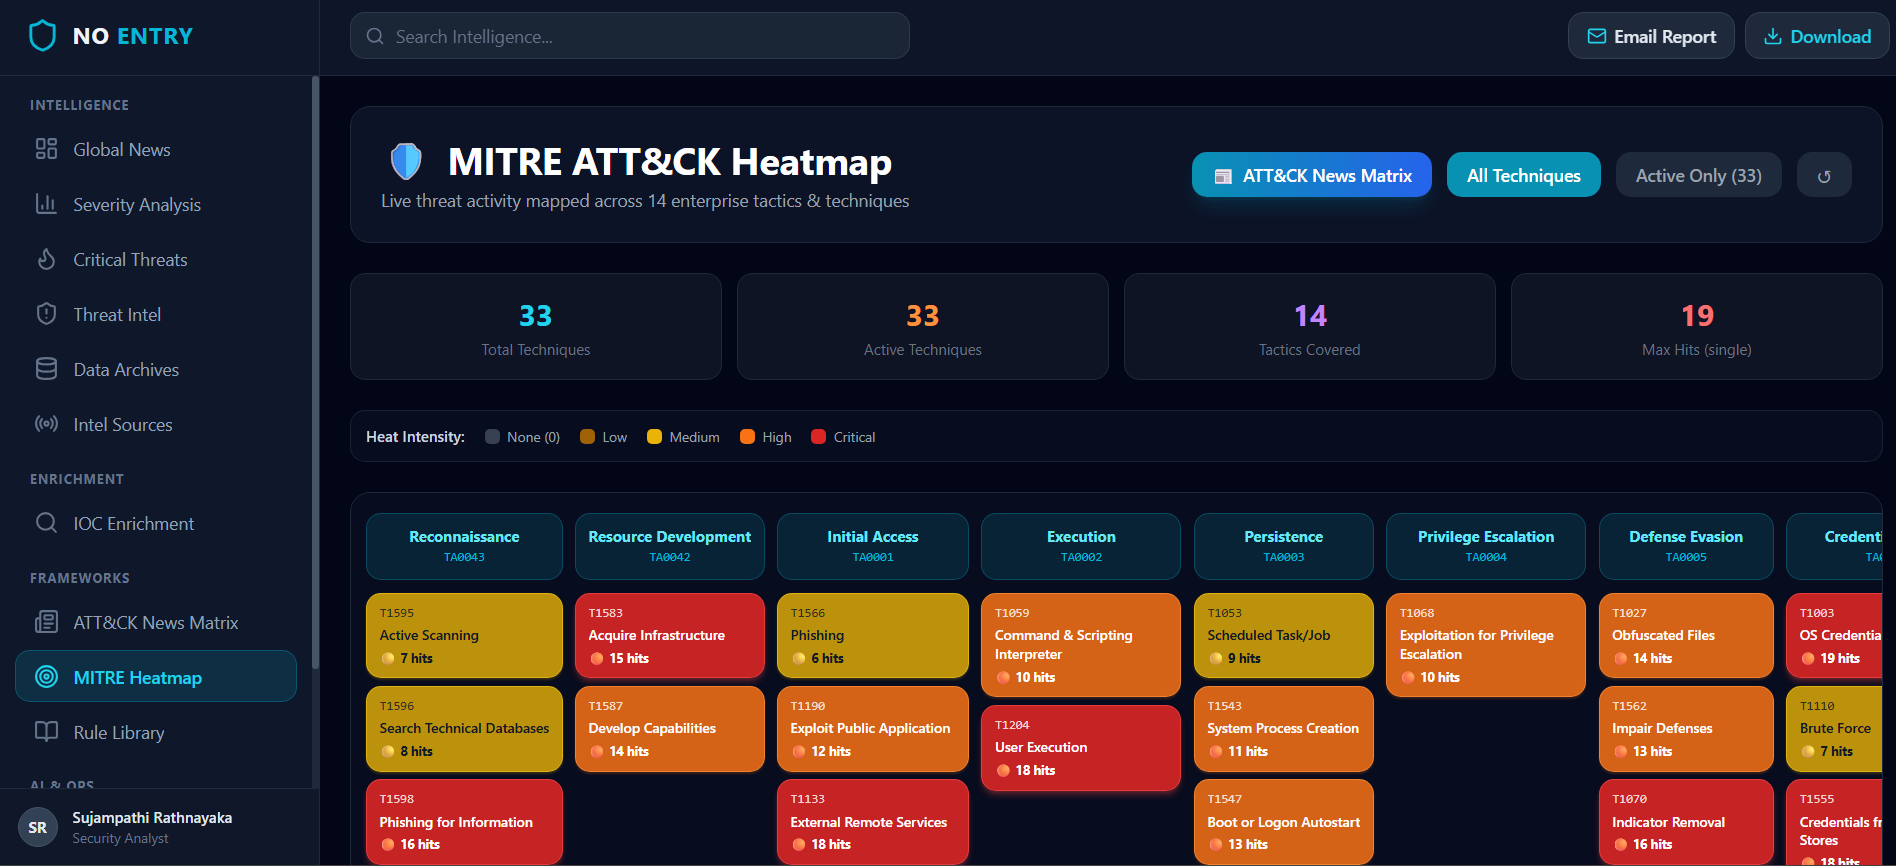
  • MITRE ATT&CK Framework
  • DDoS Detection & Mitigation

Frameworks & Compliance

  • MITRE ATT&CK Mapping
  • NIST CSF
  • ISO 27001
  • GDPR Compliance

Security & Network Tools

  • CyberArk PAM
  • Forcepoint DLP
  • NetScout Arbor
  • Darktrace
  • WAF Monitoring
  • Python & KQL Scripting
  • SOC Playbook Development

Beyond security —
creative expertise.

Graphic Design

Visual Design & Branding

Creating compelling visual identities, social media graphics, marketing materials, and brand assets that communicate clearly and leave a lasting impression.

Adobe Photoshop Adobe Illustrator Adobe Lightroom
Explore 16 Samples Below
Video Editing

Video Production & Post

Producing professional video content including cinematic edits, motion graphics, colour grading, and audio mixing for YouTube, social media, and corporate use.

DaVinci Resolve Studio Colour Grading Fairlight Audio Adobe Premiere Pro
Watch Channel Videos Below
Web Design

UI/UX & Web Development

Designing and building clean, modern, responsive websites and landing pages with a focus on user experience, accessibility, and performance optimisation.

HTML / CSS JavaScript Figma WordPress Responsive Design
Visual Portfolio

Graphic Design & Brand Identity Showcase

Selected client, university, and enterprise design works — spanning brand identities, vector illustrations, commercial print collateral, and cybersecurity awareness campaigns crafted with Adobe Creative Cloud.

TC PDR — Royal Crest & Lion Emblem Brand Identity
View Sample
Adobe Illustrator

TC PDR — Royal Crest & Lion Emblem

Luxury gold lion and crown crest emblem with precision vector geometry on royal navy gradient.

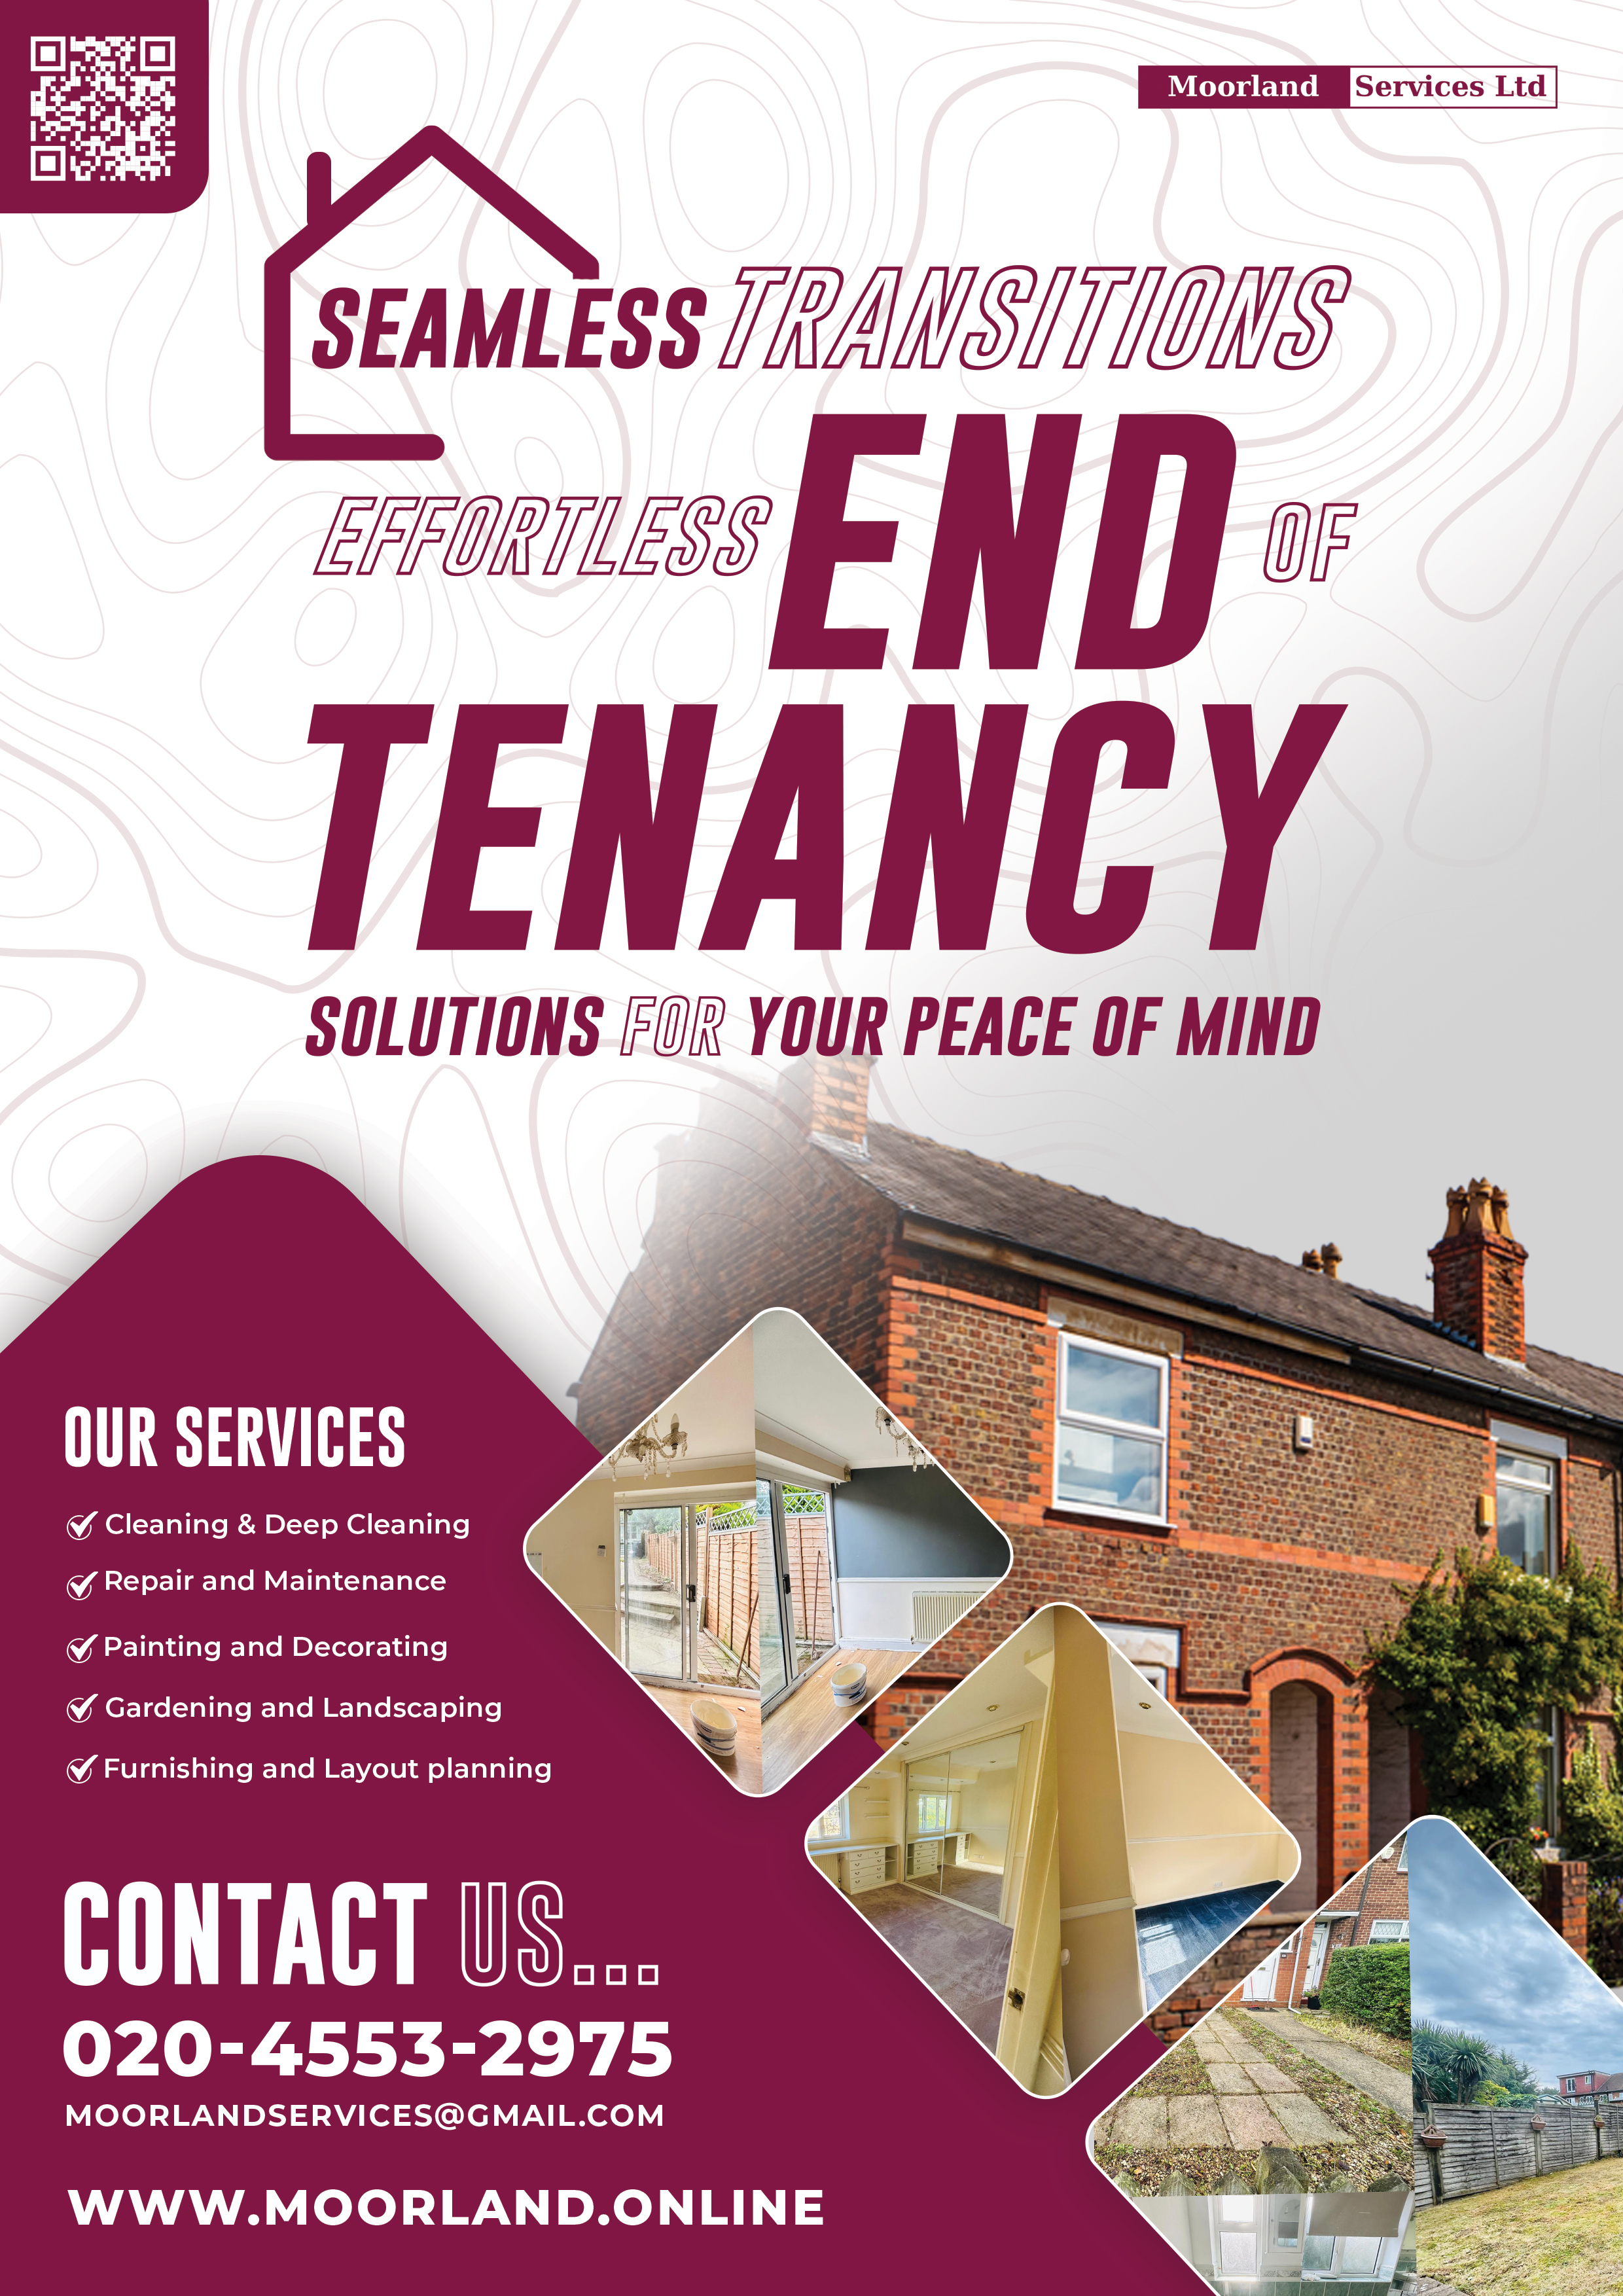
Moorland Services — End of Tenancy Flyer Flyers & Print
View Sample
Photoshop & InDesign

Moorland Services — End of Tenancy Flyer

Comprehensive real estate property management and maintenance marketing flyer with photo grid layout.

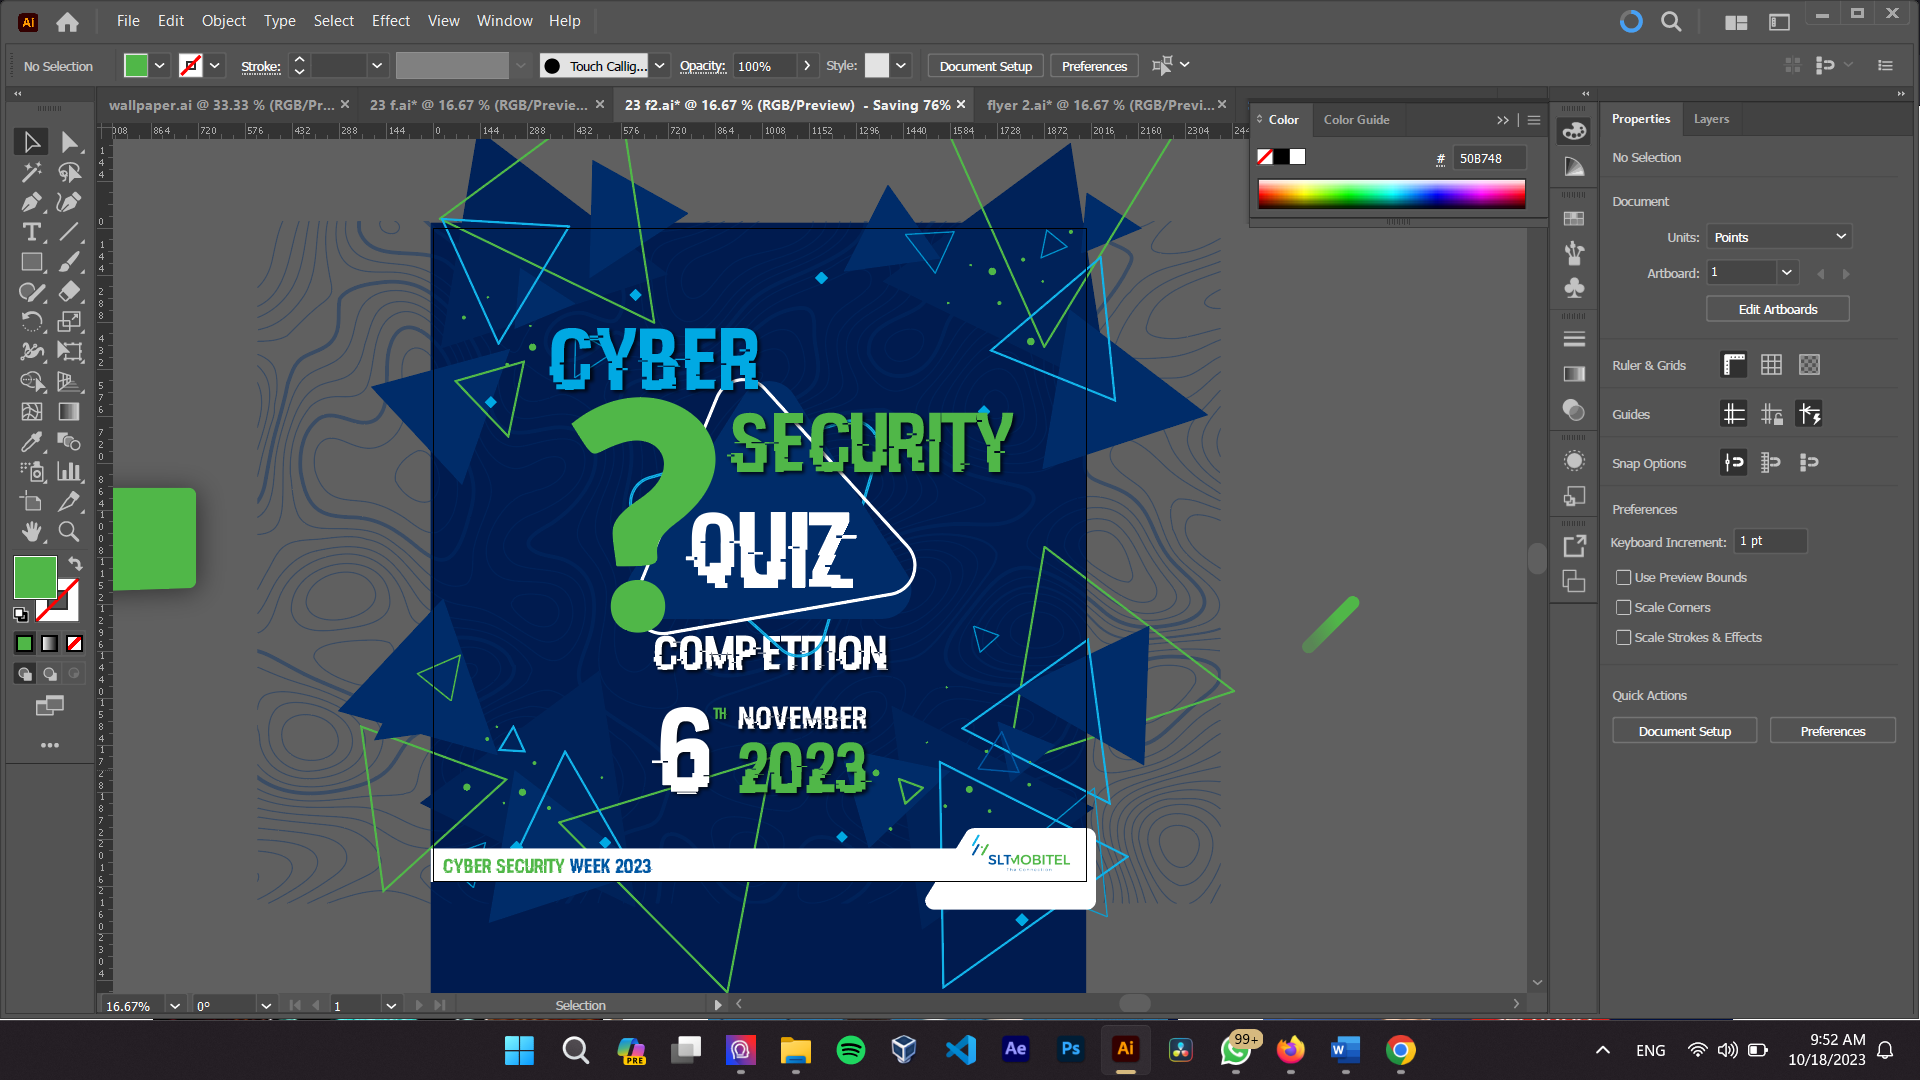
SLTMOBITEL — Cyber Security Quiz Campaign Corporate & Event
View Sample
Adobe Illustrator

SLTMOBITEL — Cyber Security Quiz Campaign

Enterprise awareness week competition poster designed for Sri Lanka Telecom (SLT-Mobitel).

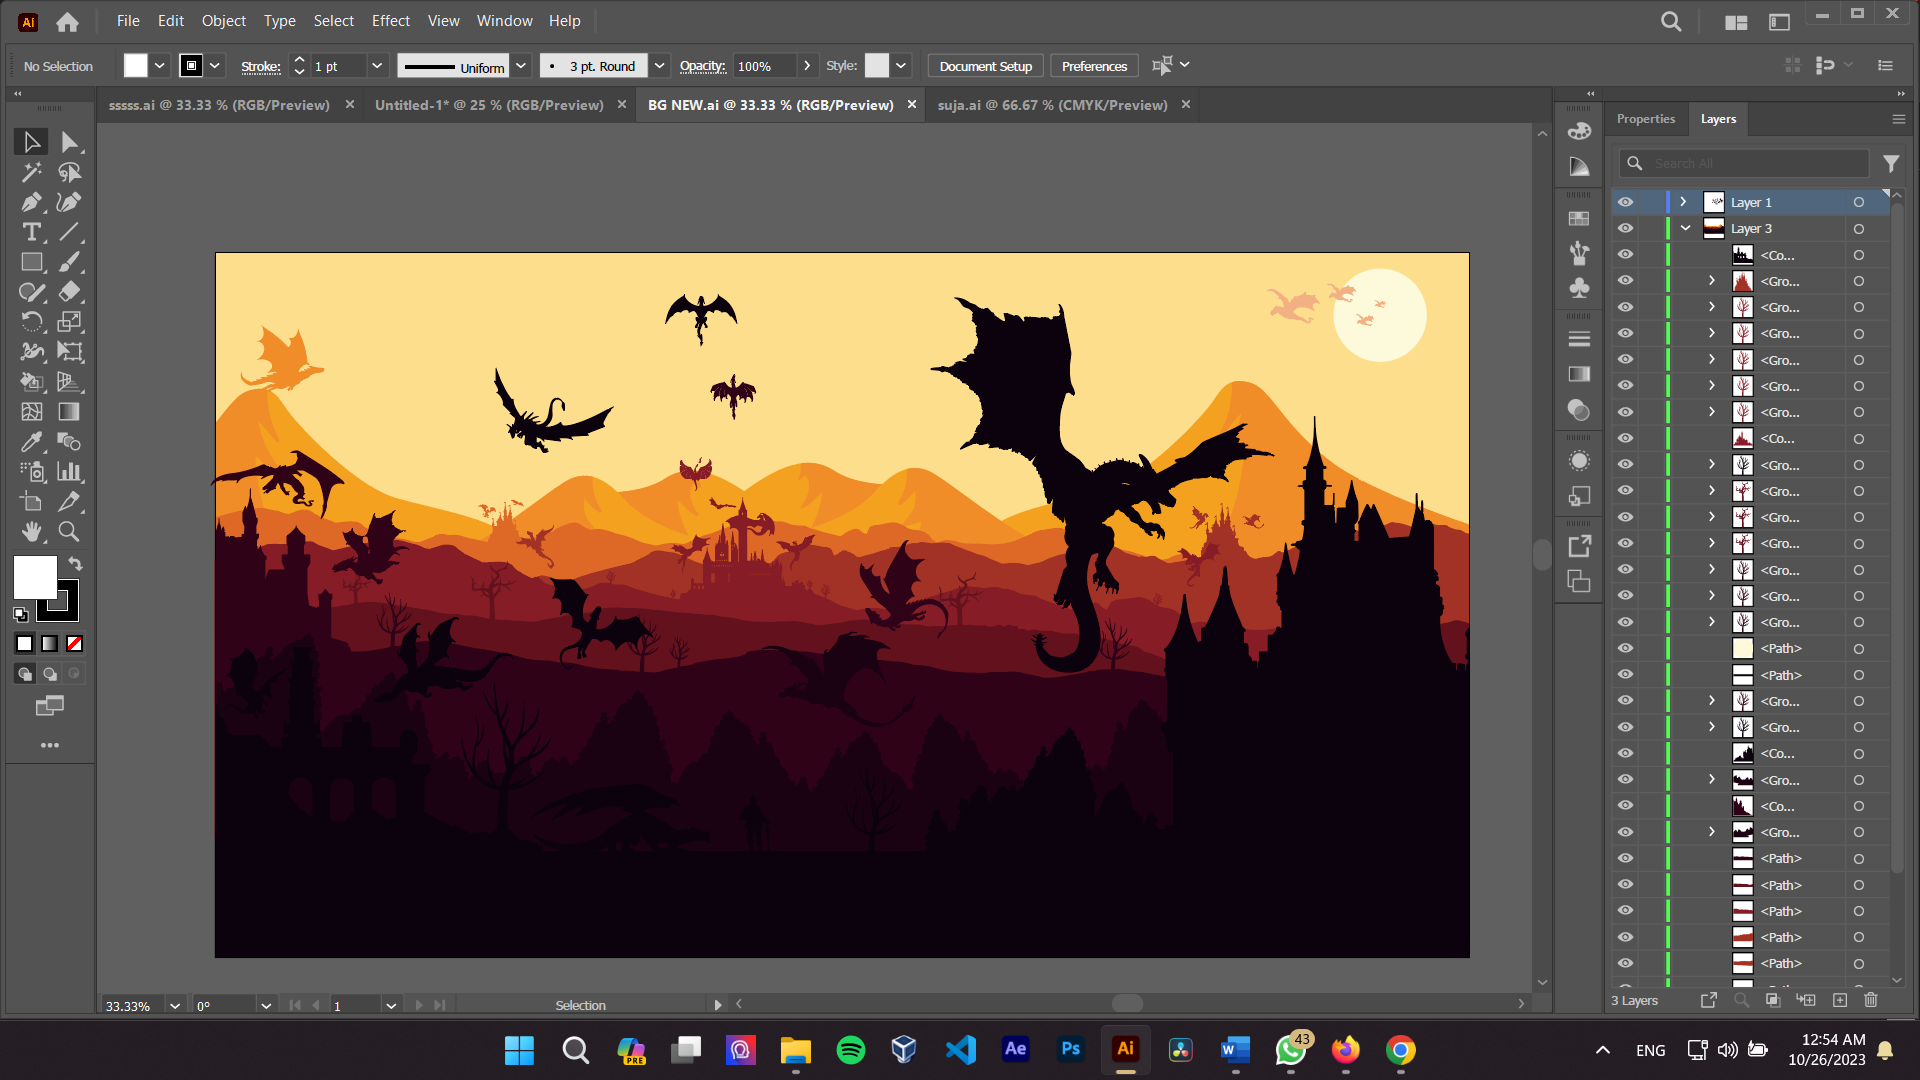
Dragon Realm Twilight — Fantasy Vector Art Digital Illustration
View Sample
Adobe Illustrator

Dragon Realm Twilight — Fantasy Vector Art

Multi-layered vector landscape artwork featuring Gothic castle spires, soaring dragons, and gradient depth.

NASA Creations — Modern Celestial Emblem Brand Identity
View Sample
Adobe Illustrator

NASA Creations — Modern Celestial Emblem

Minimalist cosmic monogram logo with dual-tone eclipse geometry and stellar accents.

Hemel Apartments — Luxury Guest Guide Flyers & Print
View Sample
Adobe Illustrator

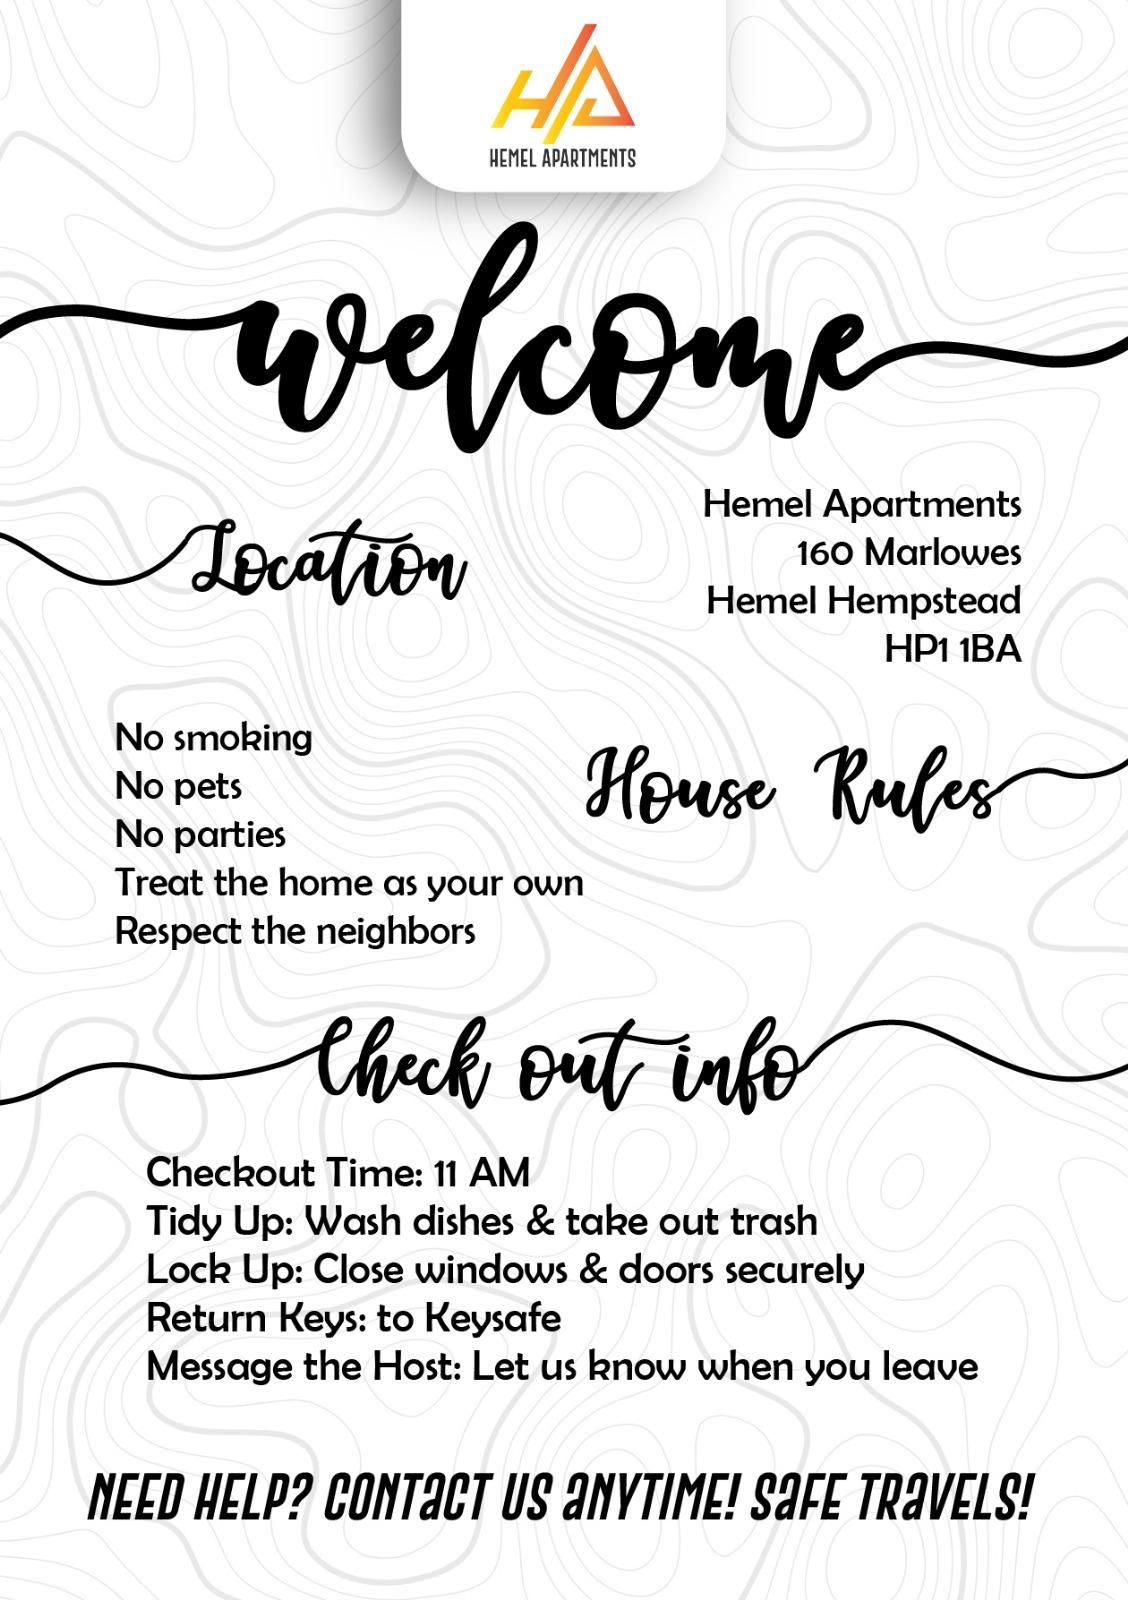
Hemel Apartments — Luxury Guest Guide

Clean hospitality house rules and check-out guide designed for serviced apartments in Hemel Hempstead, UK.

SLIIT Media Unit — Cultural Panorama Banner Digital Illustration
View Sample
Adobe Illustrator

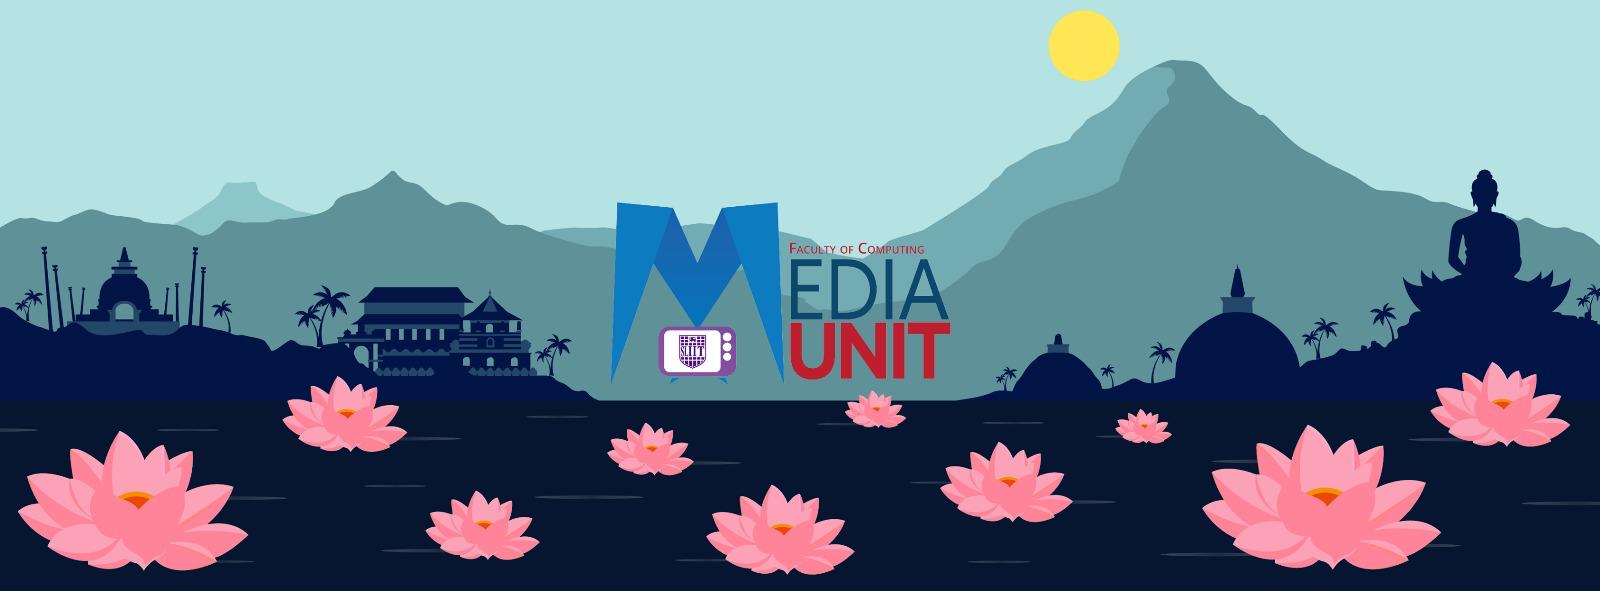
SLIIT Media Unit — Cultural Panorama Banner

Wide-format Sri Lankan cultural vector landscape illustration with stupas, lotus blossoms, and mountains.

University of Hertfordshire Sri Lankan Society Brand Identity
View Sample
Adobe Illustrator

Univ. of Hertfordshire Sri Lankan Society

Official student society identity fusing the Hertfordshire stag crest with cultural heritage motifs.

Rocket Launchpad Highway — Sci-Fi Vector Art Digital Illustration
View Sample
Adobe Illustrator

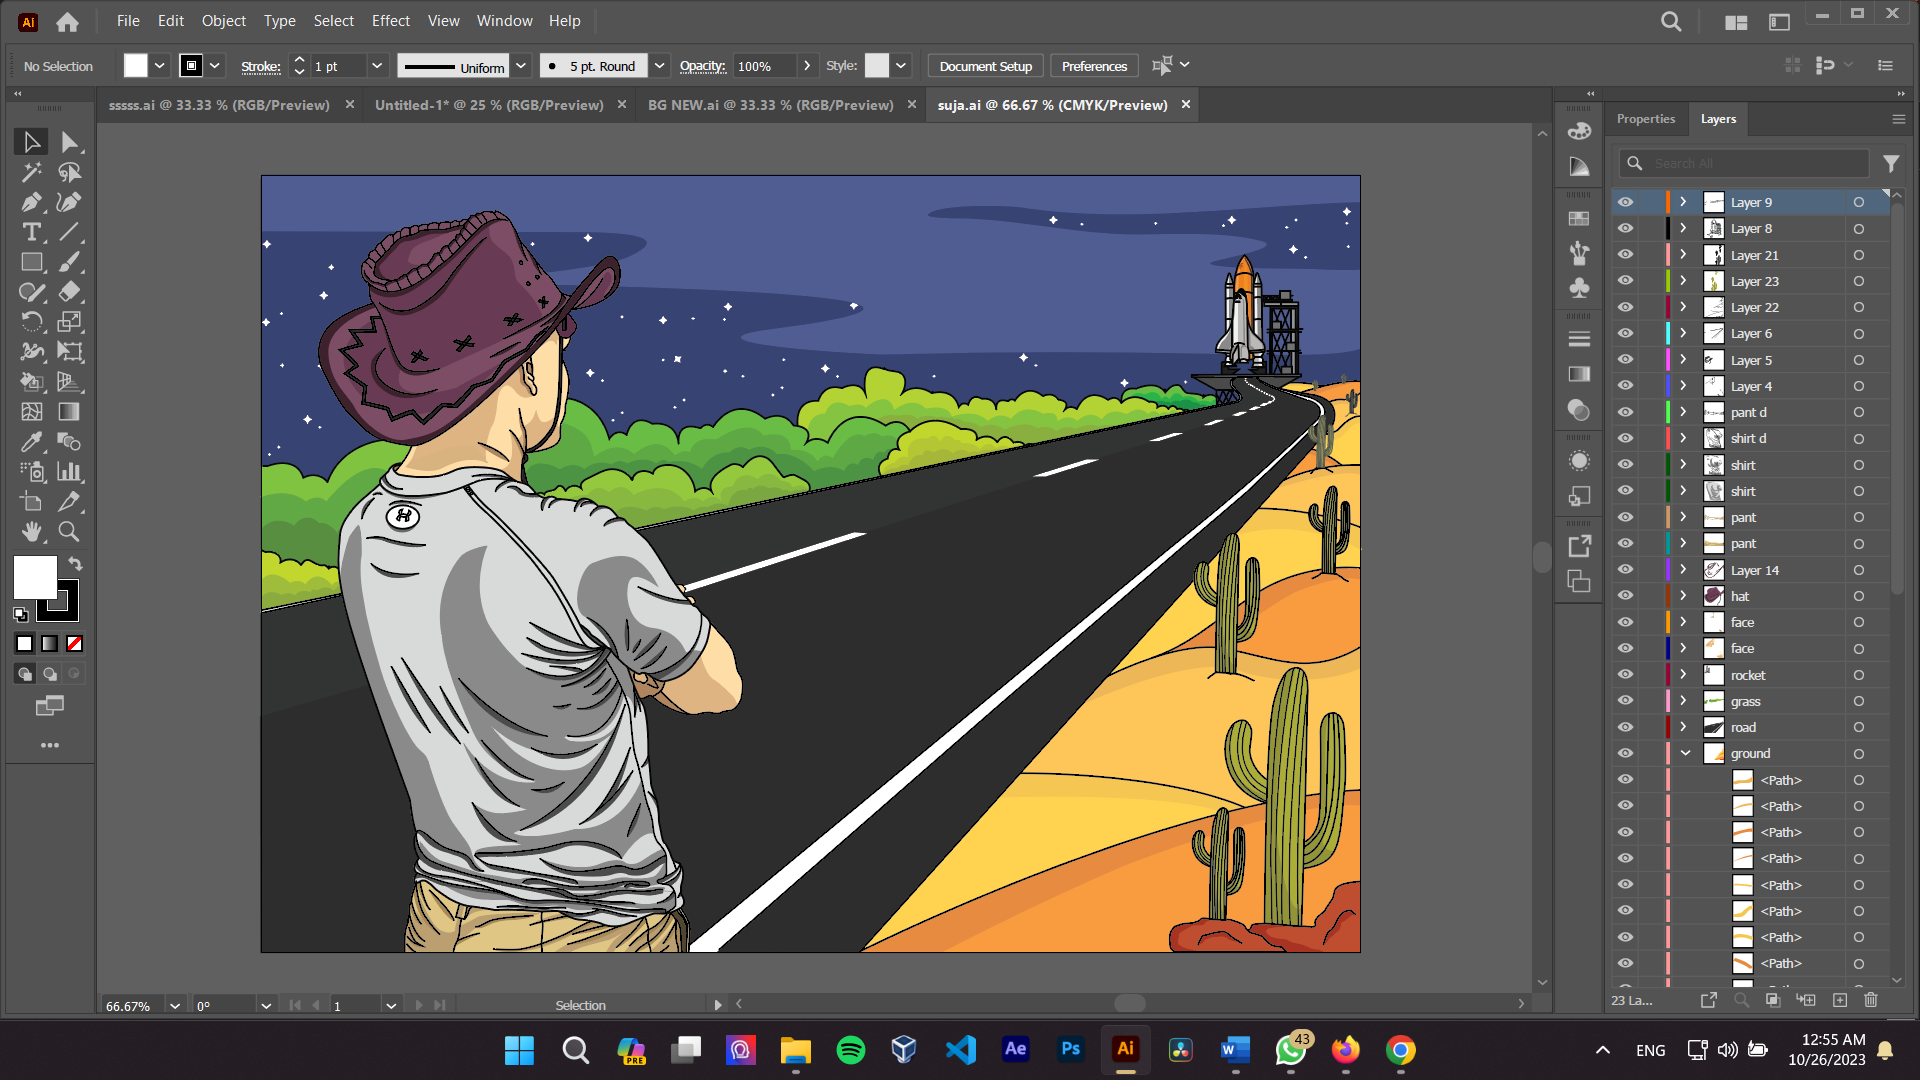
Rocket Launchpad Highway — Sci-Fi Vector Art

Original perspective character vector artwork (suja.ai) featuring desert highway horizon toward a space rocket.

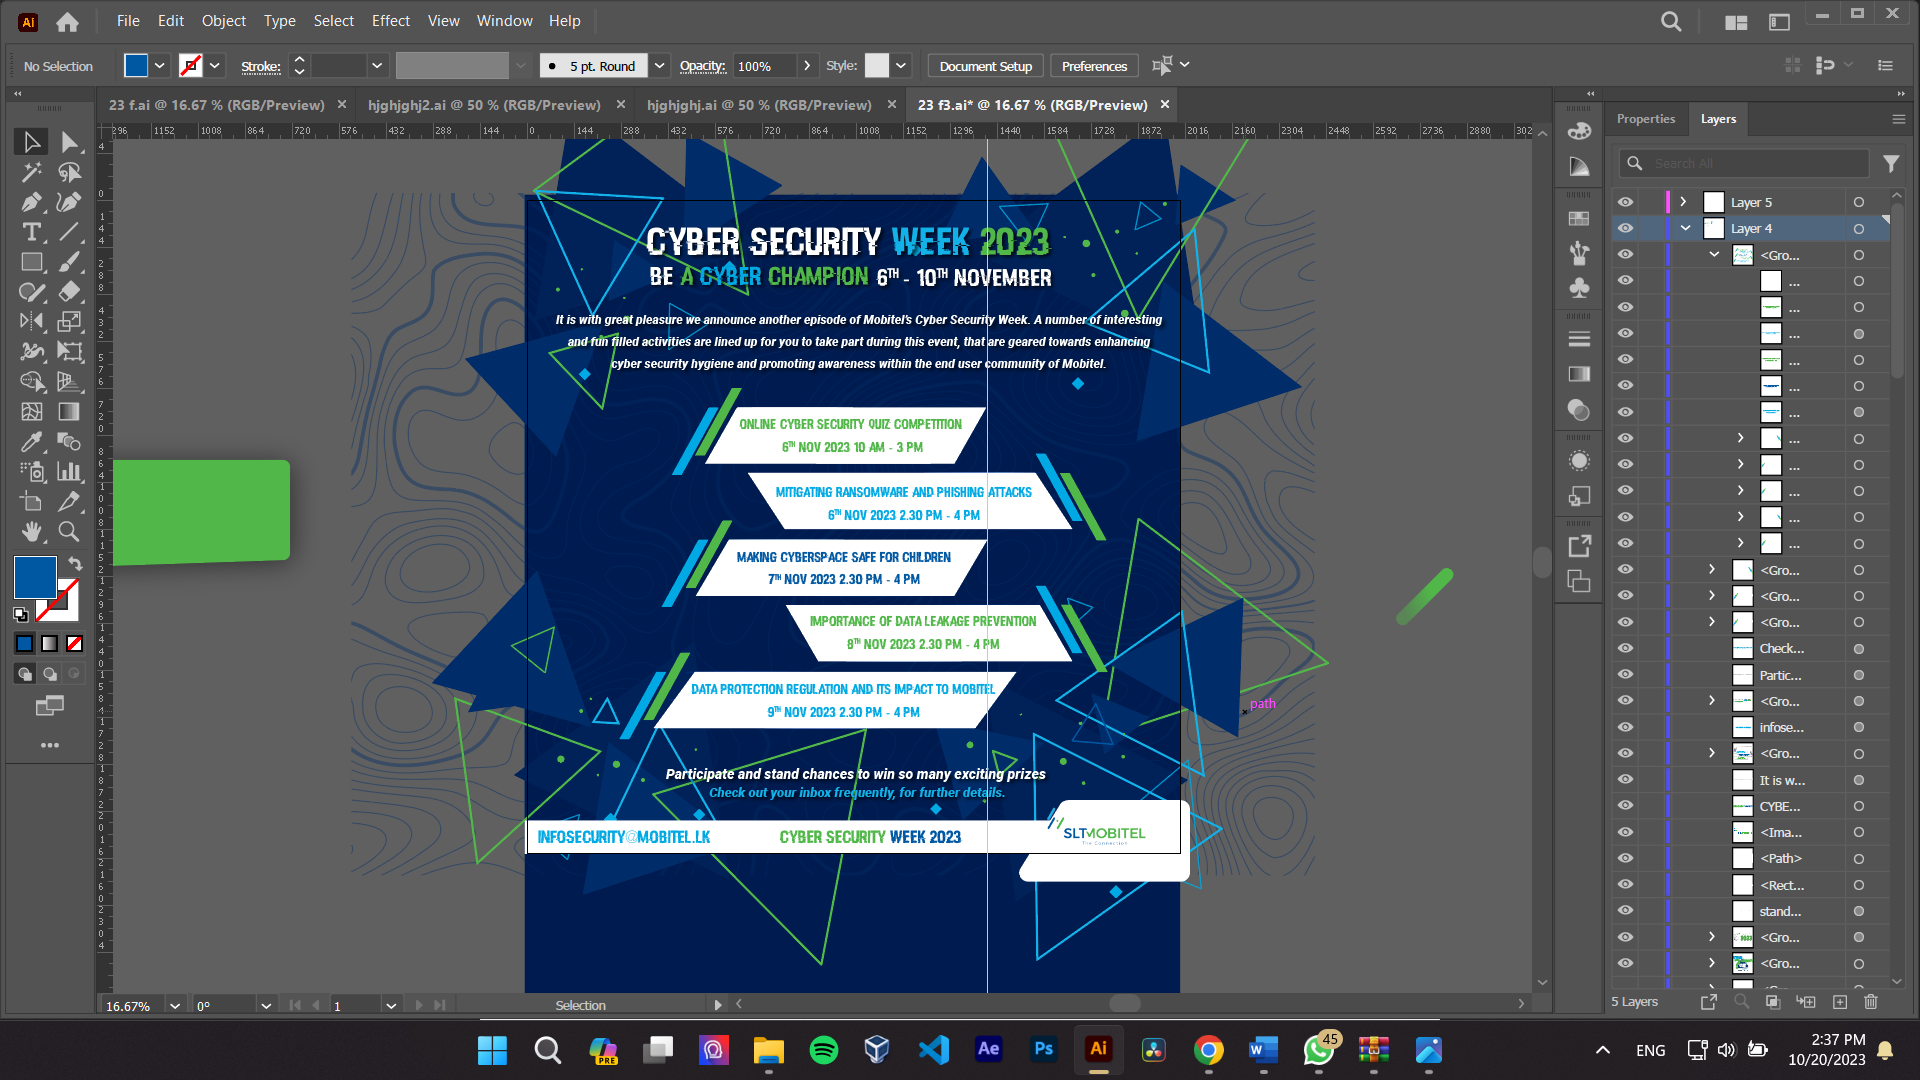
SLTMOBITEL — Cyber Week Event Schedule Corporate & Event
View Sample
Adobe Illustrator

SLTMOBITEL — Cyber Week Event Schedule

Corporate infographic schedule detailing daily threat defense tracks for SLT-Mobitel Cyber Security Week.

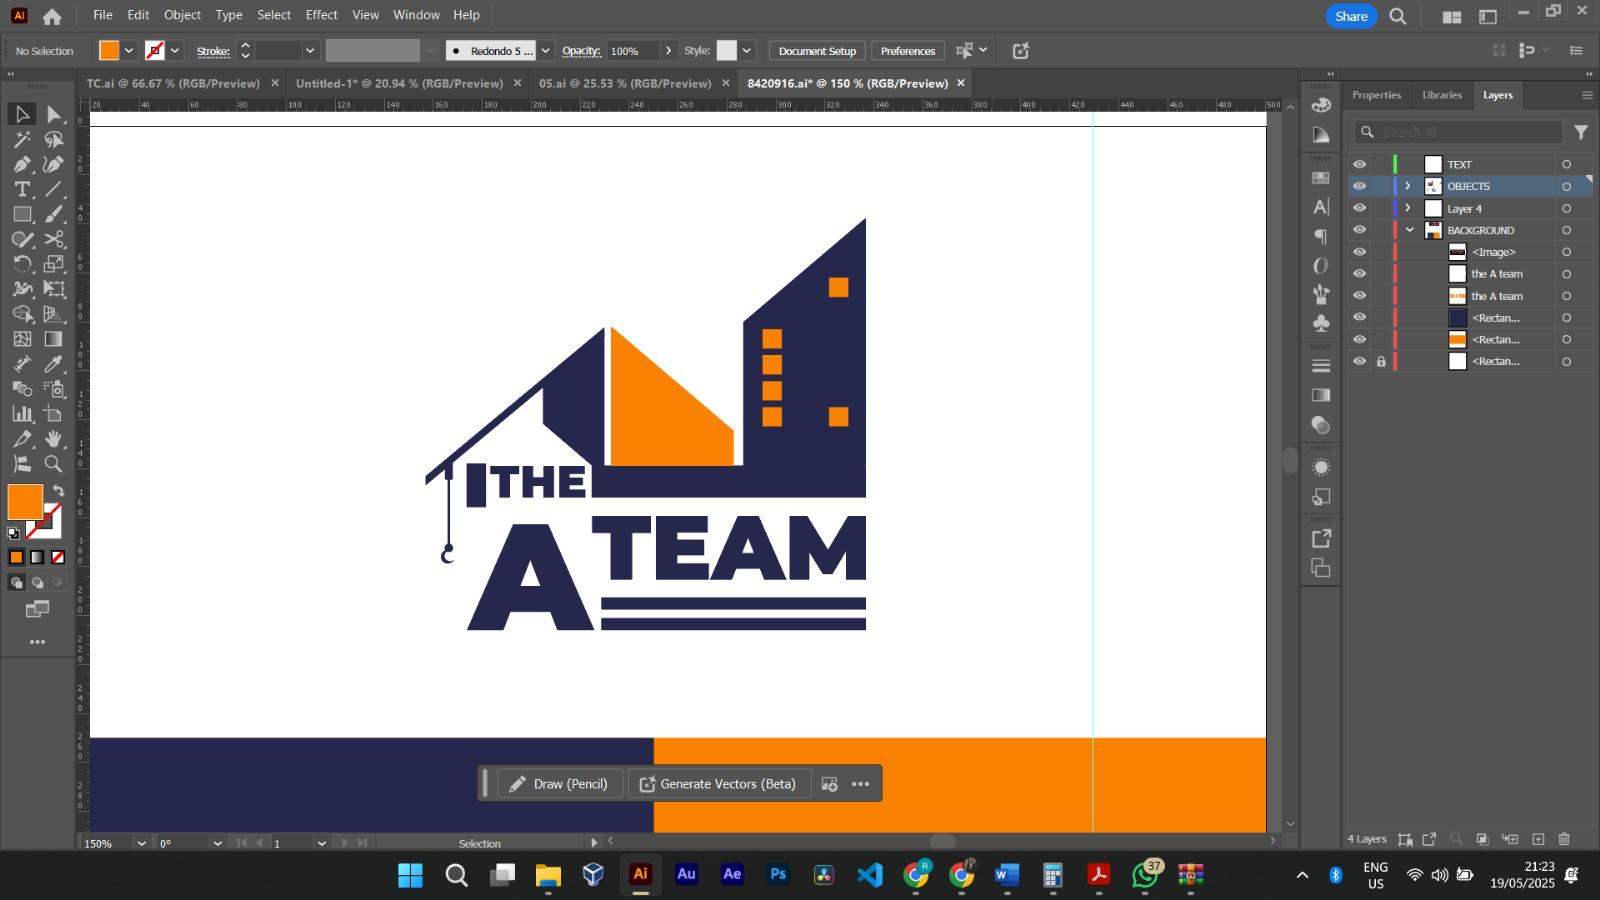
The A Team — Architecture & Developers Mark Brand Identity
View Sample
Adobe Illustrator

The A Team — Architecture & Developers Mark

Architectural skyline vector identity concept crafted in Adobe Illustrator for a property development firm.

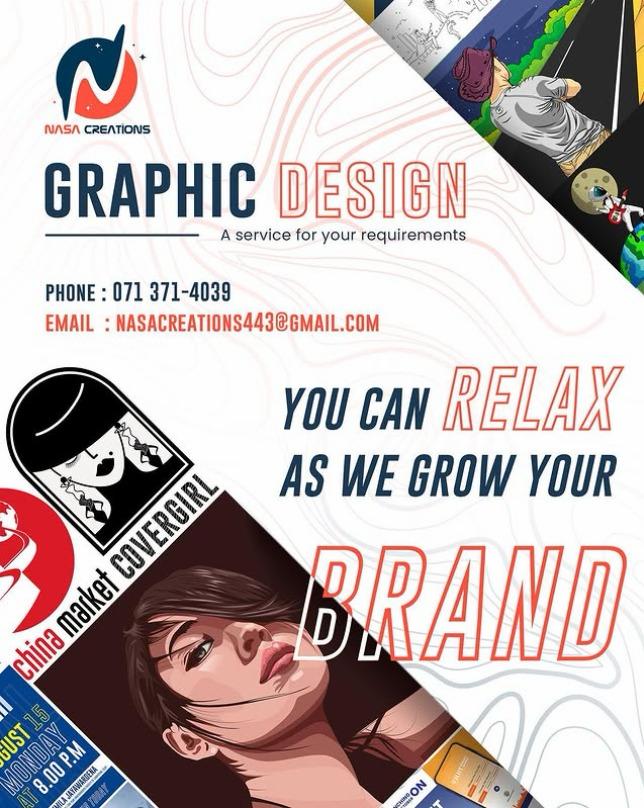
NASA Creations — Creative Services Flyer Flyers & Print
View Sample
Photoshop & Illustrator

NASA Creations — Creative Services Flyer

High-energy marketing promotional flyer highlighting branding capabilities and character artwork.

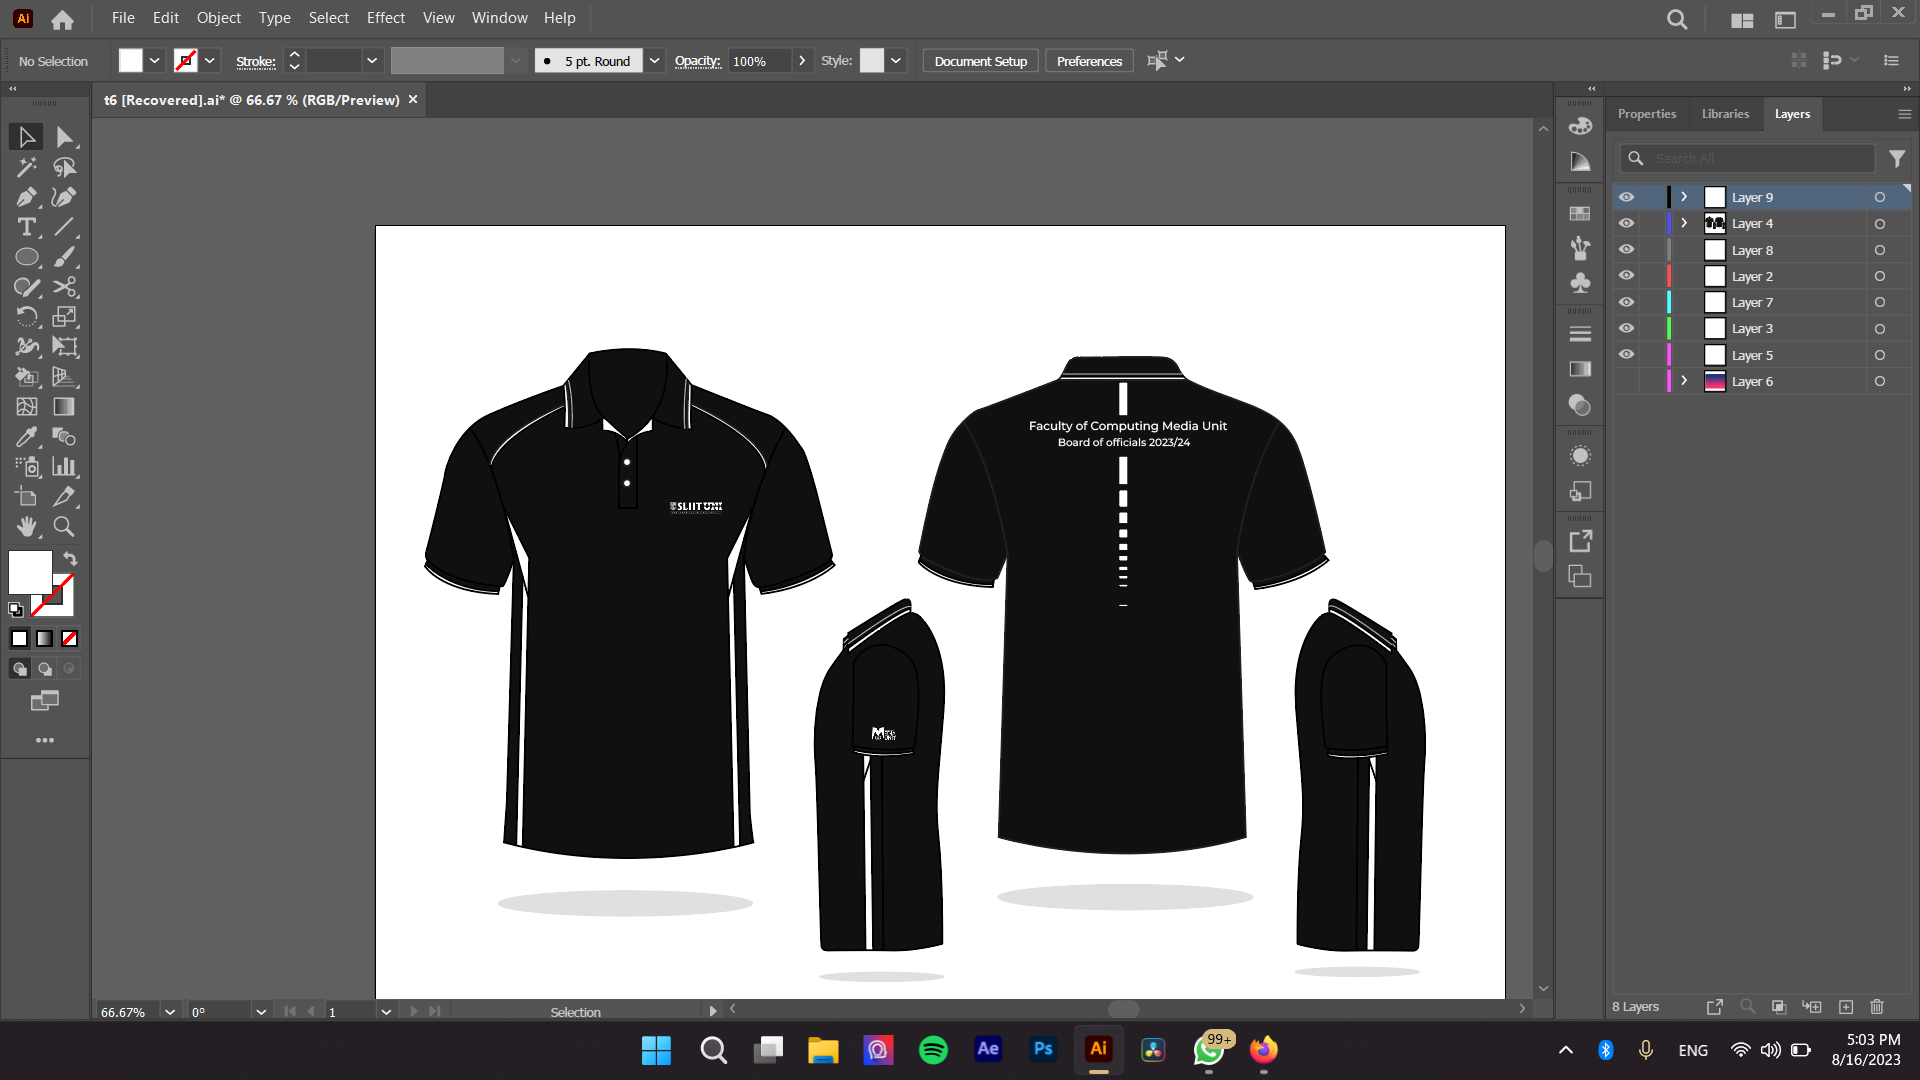
Faculty of Computing Media Unit — Polo Uniform Corporate & Event
View Sample
Adobe Illustrator

Faculty of Computing Media Unit — Polo Uniform

Technical apparel vector design and official merchandise layout for media board officials (2023/24).

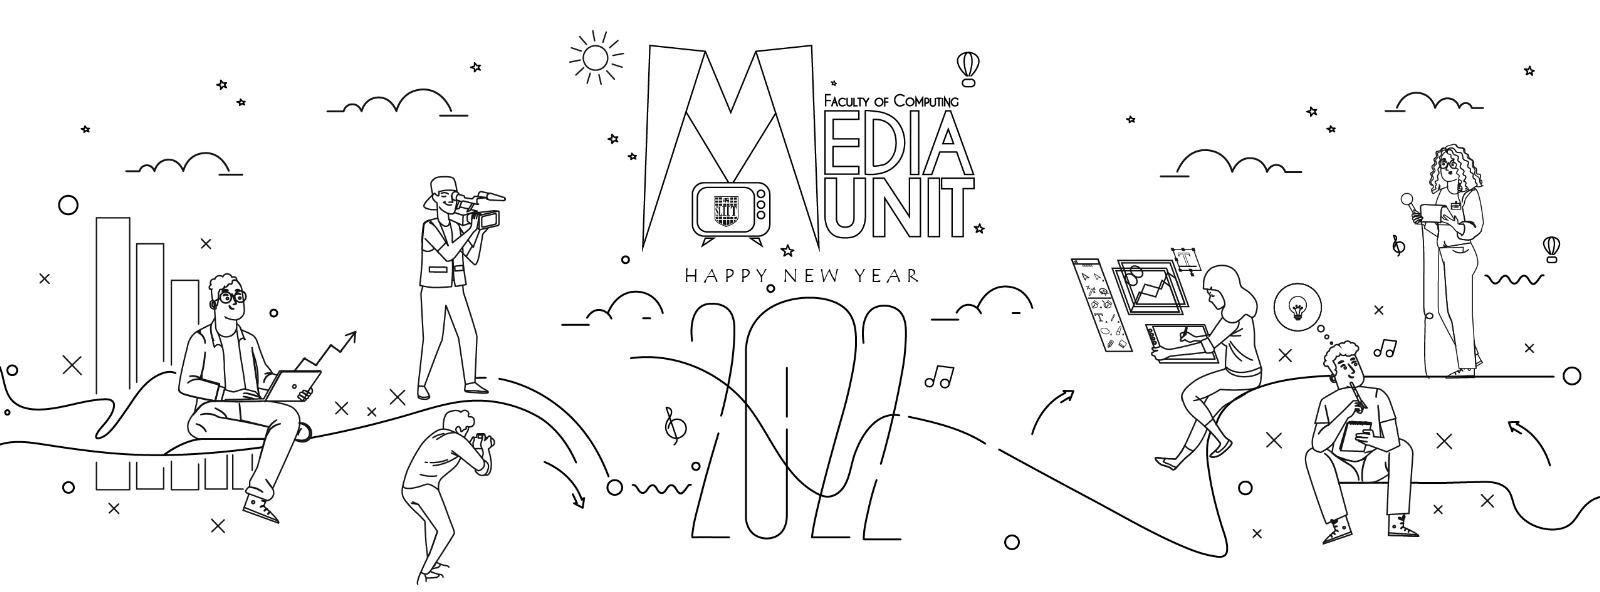
Media Unit — Creators in Action Line Art Digital Illustration
View Sample
Adobe Illustrator

Media Unit — Creators in Action Line Art

Continuous-line vector mural celebrating photographers, videographers, editors, and digital designers.

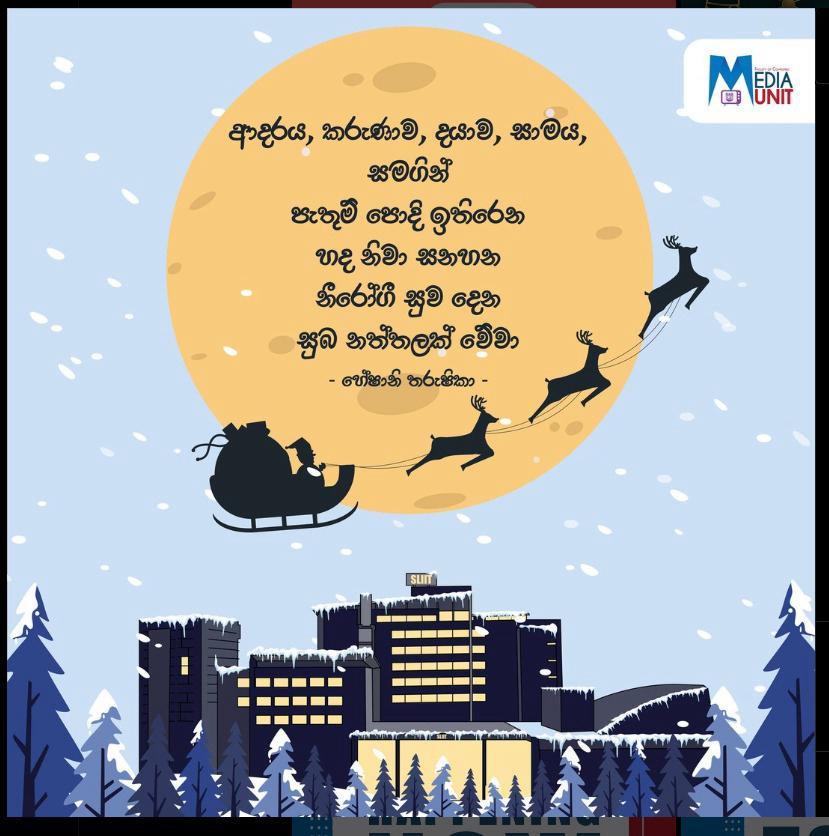
SLIIT Computing — Winter Holiday Greeting Corporate & Event
View Sample
Photoshop & Illustrator

SLIIT Computing — Winter Holiday Greeting

Seasonal digital community greetings card combining vector campus illustration and typography.

SLTMOBITEL — Cyber Glitch Typographic Concept Corporate & Event
View Sample
Adobe Illustrator

SLTMOBITEL — Cyber Glitch Typographic Concept

Cyber typographic exploration combining circuit board traces, distressed brushes, and digital glitch effects.

YouTube Channel · Life in Frames

Cinematic Video Production & Stories

Official YouTube channel showcasing 4K travel cinematography, drone perspectives, documentary landscapes, and visual stories — shot, edited, and colour graded in DaVinci Resolve Studio.

Visit @Life-in-Frames-25
Cinematic City Tour 4K Ultra HD 2:37

London Cinematic Vlog 4K | ලන්ඩන් සුන්දරත්වය 🇬🇧

Video preview thumbnail for London Cinematic Vlog 4K
Click to Play Video (Embedded Player)

Vibrant 4K cinematic city tour capturing iconic London architecture, River Thames landmarks, moody street lighting, and dynamic color grading.

Video Accessibility: High-resolution playback, Closed Captions (CC) supported, keyboard navigable (Tab / Enter / Space).
DaVinci Resolve Studio 4K Cinema Color Grading Blackmagic Color Science
Featured Channel Playlist Select any video below to load and play in the theater player
London Cinematic Vlog 4K 4K UHD 2:37
NOW PLAYING
Cinematic City Tour

London Cinematic Vlog 4K | ලන්ඩන් සුන්දරත්වය 🇬🇧

Vibrant 4K cinematic city tour capturing iconic London architecture, River Thames landmarks, moody street lighting, and dynamic color grading — edited in DaVinci Resolve Studio.

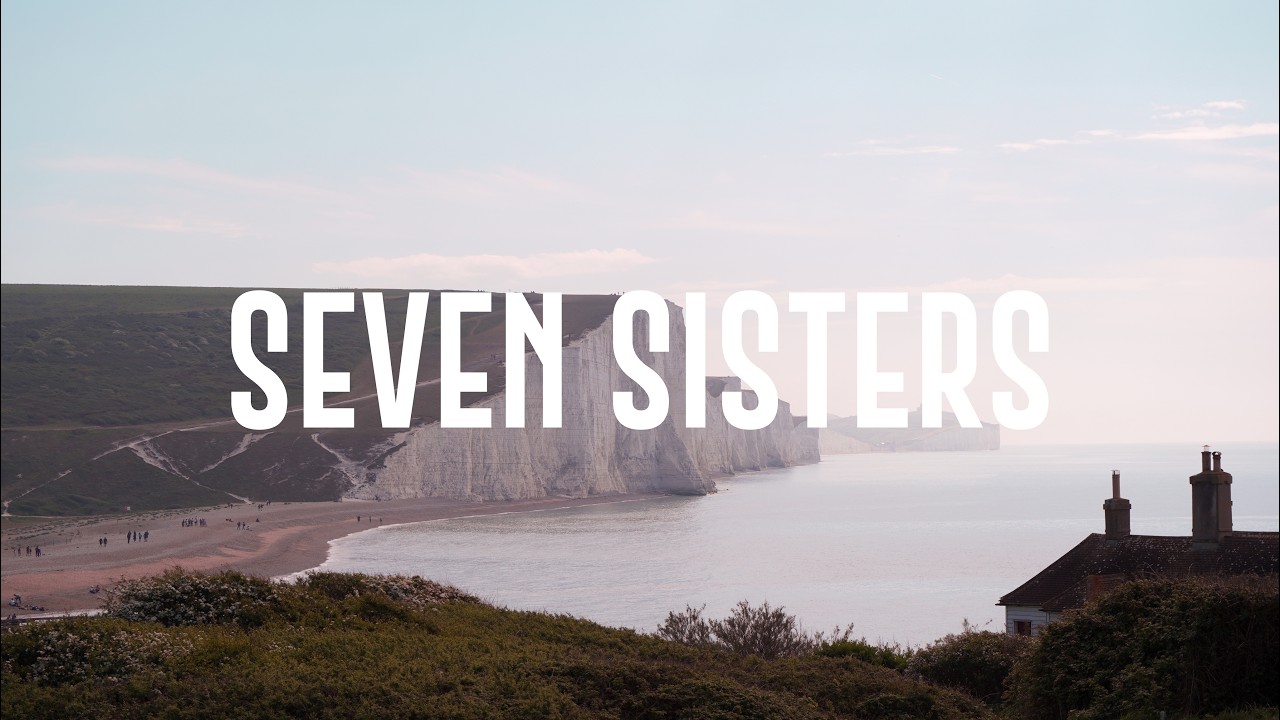
Nothing Stays Seven Sisters 4K Aerial 1:46
NOW PLAYING
Landscape & Coastline

Nothing Stays | Seven Sisters Cinematic Video

Breathtaking aerial perspectives and panoramic visuals showcasing the dramatic chalk cliffs and rolling coastal hills of East Sussex, UK — edited in DaVinci Resolve Studio.

Cherhill White Horse Drone HD 1:13
NOW PLAYING
Heritage & History

The Secret White Horses of Wiltshire! | Cherhill

Cinematic aerial exploration and documentary framing of the ancient Cherhill White Horse hill figure and Lansdowne Monument in Wiltshire — edited in DaVinci Resolve Studio.

Finding Peace in the Journey 4K Cinema 0:34
NOW PLAYING
Visual Poetry & Short Film

Finding Peace in the Journey | පොත් සහ සිතියම්

A poetic, reflective cinematic short meditating on personal journey, tranquility, exploration, and perspective — edited in DaVinci Resolve Studio.

Notable projects
with real-world impact.

6 security engineering projects built from scratch — from live production platforms to research prototypes.

02 2024–25 Zero-Trust · Machine Learning

Advanced BYOD Security Framework

Zero-trust prototype · AES-128 encryption · biometric anomaly detection

Unmanaged personal devices in corporate environments introduce severe access risks. Developed a zero-trust access control framework using AES-128 encryption with UUID-based device authorization. Trained Isolation Forest ML models and CNN-based facial recognition for biometric anomaly detection, preventing unauthorized network access from compromised endpoints.

Python AES-128 Encryption Isolation Forest ML CNN (Facial Recognition) Zero-Trust Architecture
Request Source Code
ZERO_TRUST_BYOD // ENFORCER.PY
AUTH_CIPHER: AES-128 GCM + UUID Validation ANOMALY_MODEL: ISOLATION_FOREST (0.02 Threshold) BIOMETRIC_CNN: VERIFIED (99.4% Confidence) DEVICE_STATUS: UNTRUSTED_BLOCKED ZERO_TRUST: ENFORCED → Network Isolation Active
AES-128 Encryption
99.4% Biometric Accuracy
0-Trust Architecture
DARKWEB_SCANNER // IP_ENRICHMENT.PY
TARGET_IP: 185.220.101.5 VIRUSTOTAL: MALICIOUS (42/70) ABUSEIPDB: 98% HIGH RISK DARKWEB_OSINT: C2 BOTNET HOST VERDICT: BLOCK · IOC LOGGED
42/70 VT Detections
98% AbuseIPDB Score
3 APIs Integrated
03 2023 OSINT · Threat Hunting

Dark Web IP Scanner & Threat Enrichment Tool

IP lookup time: minutes → seconds · 3 integrated threat APIs

Threat hunting requires cross-referencing suspicious IP addresses across multiple reputation engines, causing investigation latency. Built a Python automation script integrating REST APIs from VirusTotal, AbuseIPDB, AlienVault OTX and dark-web OSINT feeds — generating threat hashes, geolocation, and severity scoring in one analyst-ready summary.

Python VirusTotal API AbuseIPDB API AlienVault OTX Dark Web OSINT
Request Source Code
04 2023 SIEM Automation · Security Ops

SIEM Log Processing Automation Engine

Python log parsing · SIEM integration · brute-force detection

High volumes of unparsed raw logs flood SIEM consoles, creating alert fatigue and increasing Mean Time to Investigate (MTTI). Wrote custom Python log parsers using regex pattern matching to extract IP, user, and payload fields from raw system logs — integrating structured output pipelines directly into SIEM workflows and detecting brute-force patterns automatically.

Python Regex Parsing SIEM Integration Log Analysis Security Operations
Request Source Code
SIEM_PARSER // REGEX_AUTOMATION.PY
LOG_INGEST: 25,000 EVENTS / SEC MTTI_REDUCTION: 30% FASTER TRIAGE NOISE_FILTER: 15+ CORRELATION RULES BRUTE_FORCE: DETECTED → PORT 443 BLOCKED PIPELINE: SIEM INTEGRATED ✓
25K Events/sec
30% MTTI Reduction
15+ Custom Rules
PHISHING_AI // IMAP_FORENSICS.PY
SPF: PASS | DKIM: PASS | DMARC: FAIL GEMINI_AI: SPOOFED NAME DETECTED AI_SCORE: 0.94 MALICIOUS CTI_FEEDS: MALICIOUS URL MATCHED ACTION: QUARANTINE TRIGGERED ✓
0.94 AI Threat Score
Auto Quarantine
IMAP Real-time Scan
05 2022 Email Security · AI Analysis

AI-Augmented Phishing Detection & CTI Engine

AI score 0.94 malicious · automated quarantine · SPF/DKIM/DMARC validation

Standard email security gateways miss sophisticated phishing attacks and zero-day malicious URLs. Built a Python application using IMAP to scan incoming mail in real-time, implementing SPF/DKIM/DMARC header validation, CTI feed URL checks, and Gemini AI API contextual analysis — automatically quarantining spoofed and malicious messages with high accuracy.

Python IMAP Gemini AI API SPF/DKIM/DMARC CTI Feeds Email Forensics
Request Source Code
06 2024 Pentesting · Automation

Kali Linux CLI Pentesting Scanner

2× assessment speed · unified Nmap + Nikto + Metasploit · HTML reports

Routine vulnerability assessments require running fragmented tools individually, causing reporting delays. Built a Bash CLI tool on Kali Linux that orchestrates Nmap stealth port scans, Nikto web server probes, and Metasploit auxiliary modules in a single command — consolidating outputs into structured, analysis-ready HTML reports.

Kali Linux Bash Scripting Nmap Nikto Metasploit
Request Source Code
KALI_CLI // PENTEST_RECON.SH
NMAP_STEALTH: PORTS 22, 80, 443 OPEN NIKTO_WEB: CVE-2023-XXXX DETECTED METASPLOIT: AUX MODULE EXECUTED RISK_SCORE: HIGH — 3 Low, 1 High REPORT: HTML GENERATED ✓
2× Faster Recon
3-in-1 Tool Chain
HTML Auto Reports

Cyber Insight — The Digital Watch
Clear insight into the digital world.

Independent cybersecurity research and practical threat intelligence published from the SOC floor — breaking down real-world enterprise breaches, AI threats, voice cloning, and digital defense tradecraft in plain English.

Active Editorial Publication · 10-Part Series & Case Studies

Cyber Insight

Cyber Threat Intelligence · Digital Literacy · Forensic Incident Analysis

Everyone talks about cybersecurity in technical terms. Cyber Insight (The Digital Watch) cuts through the jargon to explain what's actually happening online — simply, honestly, and in plain language. Written from 2.5+ years of Tier 1 & Tier 2 SOC operations to bridge technical defensive knowledge with everyday digital literacy.

10-Part Editorial Curriculum: Structured deep-dives into phishing, synthetic identities, deepfakes, and endpoint defense.
Behind the Breach Case Studies: Forensic post-mortems investigating real attacks (e.g. Manchester Airports Group breach), mapping attack paths and defense failures.
Plain-English Literacy: Translating complex MITRE ATT&CK techniques and IOCs into clear, actionable advice for security teams and everyday internet users.
Topics Covered:
🛡️ Digital Defense 🤖 AI Voice Cloning & Deepfakes ✈️ Aviation & Telecom Breaches 🎯 Threat Intelligence & IOCs 🎣 Anti-Phishing Tradecraft 📖 Plain-English Security

Certifications & Awards

What I'm working on
right now.

Scheduled

Microsoft SC-200: Security Operations Analyst

Scheduled certification focused on Microsoft Sentinel, Microsoft Defender XDR, KQL threat hunting, incident detection & response, and SOC correlation rule tuning.

Timeline: Scheduled Nov 2026 Priority: High
In Progress

TryHackMe – SOC Learning Path

Actively following the TryHackMe SOC Learning Path with daily hands-on practical labs, focusing on SIEM alert analysis, log investigation, threat detection, and incident response in real-world SOC scenarios.

Timeline: Ongoing Priority: High
Upcoming

Wazuh Policy Implementation

Implementing and testing Wazuh security policies using Kali Linux, including log analysis, rule tuning, agent configuration, and threat detection use cases.

Timeline: Planned Priority: Medium
Upcoming

Custom SOC Lab Environment

Designing and building a custom SOC lab environment on Kali Linux, integrating SIEM, endpoint monitoring, threat simulation, and incident response workflows for hands-on SOC practice.

Timeline: Q3 2026 Priority: Medium

Academic
Background.

University of Hertfordshire Logo

MSc Cyber Security

University of Hertfordshire, UK

NCSC Certified MSc

2024 – 2025  ·  NCSC Certified Master's Degree

  • Completed an NCSC Certified MSc in Cyber Security, including study in incident response, digital forensics and security operations
  • Covered distributed systems security, information security management & compliance, digital forensics, penetration testing, and cyber operations
  • Critically evaluated vulnerabilities and threats — conducting comprehensive risk assessments in complex enterprise environments
SLIIT Logo

BSc(Hons) Information Technology
Specialized in Cyber Security

Sri Lanka Institute of Information Technology (SLIIT)

Completed

2020 – 2024  ·  Specialization in Cyber Security

  • Core studies in networking, information security, software engineering, and database systems
  • Specialization in Cyber Security — covering threat detection, network defence, and security operations
  • Final year project focused on BYOD Security using machine learning (Enhanced Security In a BYOD Environment)

Let's build something
secure together.

I'm actively looking for SOC Analyst opportunities in the UK. Whether you're a recruiter, a hiring manager, or a fellow security professional — feel free to reach out!

Blog / Threat Research Cyber Insight (The Digital Watch) ↗
YouTube (Life in Frames) youtube.com/@Life-in-Frames-25
Phone / WhatsApp +44 7768 875587
Location

Hatfield, United Kingdom